Manufacturing External Compliance Standards: Building an Audit Checklist
An audit checklist is only as reliable as the requirements behind it. A factory can hold a valid management-system certificate and still fail a product conformity assessment, breach a local safety requirement, or ship goods that do not meet a customer’s specification. These obligations overlap, but they are not interchangeable.
A workable checklist connects each applicable requirement to a defined operation, an objective acceptance criterion, and retrievable evidence. Building that connection requires more than collecting manufacturing external compliance standards: it requires deciding which rules apply, where responsibility sits, and what evidence is sufficient to support a pass, a finding, or a release hold.
Establish which obligations actually apply
“External compliance” covers several sources of requirements. Combining them into one undifferentiated list creates two problems: mandatory obligations can disappear among voluntary commitments, while irrelevant requirements consume audit time.
ISO 9001, ISO 14001, and ISO 45001 address quality, environmental, and occupational health and safety management systems respectively. Certification against one does not establish compliance with every applicable law or certify every product made at the site. The certificate’s scope, covered locations, validity, and issuing body therefore matter more than the presence of a certificate logo.
Technical standards also need careful treatment. A standard may be voluntary in one context but become relevant through legislation, a contract, or a selected conformity assessment route. For example, certain harmonised standards can support a presumption of conformity with specified EU legal requirements when the relevant conditions are met. That does not make every European standard mandatory, nor does it remove the need to assess all applicable product obligations.
Define the audit boundary before selecting questions
A checklist labelled “factory compliance” is too broad unless its boundaries are explicit. Record the legal entity, site, production lines, product families, outsourced processes, destination markets, and period under review. Include the company’s role where relevant: a manufacturer, importer, and distributor can have different obligations for the same product.
Separate workplace requirements from product-market requirements. Local rules govern matters such as machinery use, occupational exposure, fire protection, and environmental permits at the manufacturing site. Destination-market rules can impose separate requirements on product design, restricted substances, marking, documentation, or market access. Passing one set of checks cannot establish compliance with the other.
Product configuration is another boundary. Two products sharing a commercial name may use different materials, power supplies, firmware, or safety components. Evidence supporting one configuration may not cover the other. The checklist should identify the controlled model, drawing revision, bill of materials, or other configuration reference that connects the audit evidence to the goods being assessed.
Build an applicability register before drafting inspection questions. Each entry should record:
- The issuing authority or requirement owner, source document, clause, and applicable revision.
- The affected site, product, process, market, and legal role.
- The reason the requirement applies, including relevant exemptions or thresholds.
- The effective date and any transition arrangements.
- The responsible owner and the controls or records that demonstrate compliance.
Use official regulatory publications, standards-body sources, permit conditions, and controlled customer documents. Summaries can help identify changes, but should not replace the authoritative requirement. Where applicability is unresolved, record the open decision and assign it to a qualified owner rather than silently marking the item “not applicable.”
Convert requirements into observable audit tests
A question such as “Are machines safe?” produces an opinion rather than a reproducible finding. A useful checkpoint identifies the equipment or activity, the applicable control, the method of verification, and the acceptance basis.
For a guarding requirement, this could mean checking the specified machine against its approved guarding design and applicable criteria, examining maintenance records, and verifying protective functions through an authorized procedure. Functional testing must be planned so that the audit itself does not expose anyone to moving parts, electrical energy, or an unexpected restart.
Keep separate obligations separate. A single question asking whether equipment is “guarded, maintained, inspected, and operated by trained employees” hides partial failures. Each control can have different evidence, ownership, and corrective action.
The chain should remain traceable from requirement to control, from control to evidence, and from evidence to the audit conclusion.
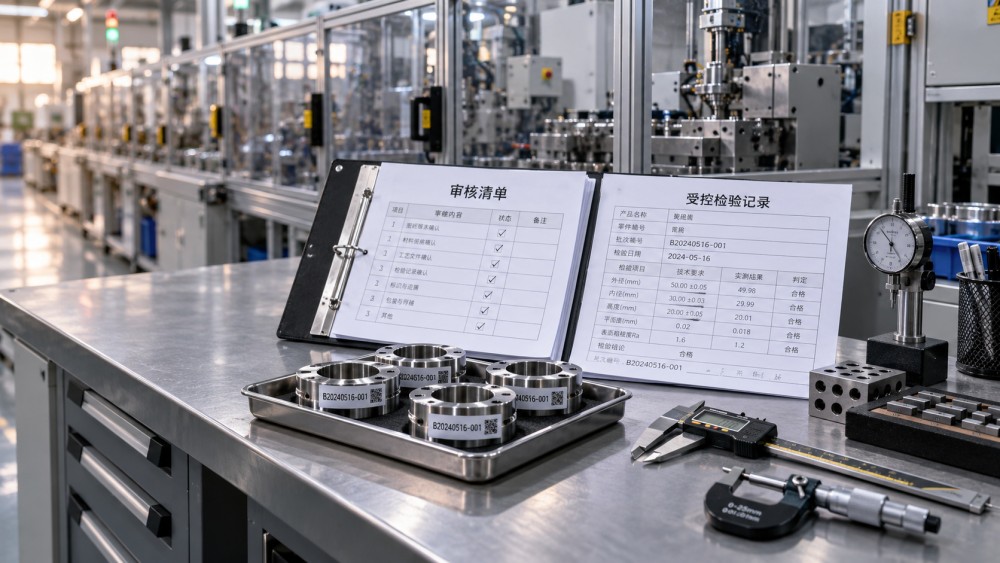
A practical checklist can use the following record structure. The examples illustrate how to frame questions; they do not establish universal legal requirements.
Each live checklist row also needs a unique identifier, source reference, owner, result, evidence location, and finding reference. “Pass,” “fail,” “not applicable,” and “not verified” should have distinct meanings. Missing evidence is not a pass, and a requirement that was not checked is not automatically inapplicable.
Choose evidence that proves implementation, not just documentation
A procedure shows what should happen. A completed record shows what was recorded. Neither alone proves that the control operated effectively. Stronger audit conclusions connect document review with observation, record tracing, and interviews where relevant.
For example, a training attendance sheet establishes attendance, not necessarily competence. If a task requires demonstrated capability, examine how authorization was granted and maintained. Similarly, a calibration label does not establish that an instrument has suitable range, resolution, or measurement uncertainty for the tolerance being accepted.
External reports require the same scrutiny. Confirm that a laboratory report covers the correct sample, method, product configuration, and relevant criteria. Where accreditation is required or relied upon, check that the method falls within the laboratory’s applicable accreditation scope. A report’s existence does not establish that every subsequent production batch conforms.
Evidence references should allow another authorized person to retrieve the same record. Use document identifiers, revisions, dates, lot numbers, equipment numbers, and controlled repository links. Avoid entries such as “certificate checked” or “records available,” which leave the conclusion difficult to reproduce.
Use risk to allocate audit effort without diluting obligations
Risk-based auditing determines where to investigate more deeply; it does not turn mandatory requirements into optional ones. A serious safety defect cannot be offset by high scores for housekeeping or document formatting.
Increase audit depth where failure could cause severe harm, prevent lawful market access, affect multiple product families, or remain undetected until after shipment. Changes deserve particular attention: a new material source, subcontractor, production location, software revision, or safety component can invalidate assumptions behind existing evidence.
Sampling should reflect those differences. Select records across relevant shifts, lines, product variants, and suppliers rather than choosing only the most accessible files. Include changed processes, prior failures, and exceptional transactions such as rework or emergency purchasing. Record what was sampled and why; there is no universal sample size that proves compliance across all manufacturing operations.
Some controls require complete verification rather than an audit sample, whether because of a legal obligation, an approved inspection plan, or a release condition. Auditing a sample of records must not be confused with performing required production inspection.
Make findings drive containment and verified correction
A finding should state the requirement, the observed condition, and the objective evidence connecting them. “Traceability is weak” is difficult to act on. “The selected finished-goods lot could not be linked to the required incoming material record” identifies a testable gap, provided the requirement and sampled lot are referenced.
Distinguish immediate containment from permanent corrective action. Containment may involve stopping equipment, segregating stock, suspending release, or assessing affected shipments. The appropriate response depends on the hazard, legal obligation, and affected scope—not simply the audit score.
Assign each finding an accountable owner, a risk-based deadline, and explicit closure criteria. Root-cause analysis should explain why the control failed, including why existing detection mechanisms did not prevent or identify the failure. “Operator error” is not an adequate explanation if instructions, access permissions, equipment design, or production pressures remain unexamined.
Closure requires more than an uploaded procedure or a purchase order for replacement parts. Verify implementation, then check effectiveness after a suitable operating period or production cycle. Where relevant, assess earlier production and determine whether customer communication, regulatory reporting, withdrawal, or recall obligations arise. Those decisions require the applicable legal and contractual criteria.
Keep the checklist synchronized with operational change
An annual review alone cannot keep a checklist aligned with every meaningful change. Link updates to engineering changes, supplier substitutions, new destination markets, permit amendments, regulatory revisions, and revised customer agreements. Assign responsibility for monitoring each source and translating changes into affected controls.
Version control should preserve what was audited, against which requirements, and on what date. When an obligation changes, identify affected inventory, work in progress, technical documentation, training, and release rules. Replacing the checklist file without evaluating those consequences leaves the operational gap intact.
The final measure of a checklist is whether it supports defensible decisions. For any critical product, process, or shipment, the records should show which requirements applied, how they were verified, what remained unresolved, and who authorized the resulting action. Where that chain is incomplete, the gap needs an explicit decision—not an assumed pass.
Weekly Insights
Stay ahead with our curated technology reports delivered every Monday.
Recommended News
 Supply ChainOct 27, 2026How to account for chargeable weight in air freight cost analysis
 Supply ChainOct 27, 2026USTR Proposes Extending Pause on China Maritime Trade Measures to January 2027
 Market TrendsOct 26, 2026How industrial import-export analysis reveals shifts in demand
 Industry StandardsOct 27, 2026What Are the Main Risks of Rail Freight for High-Value Cargo?